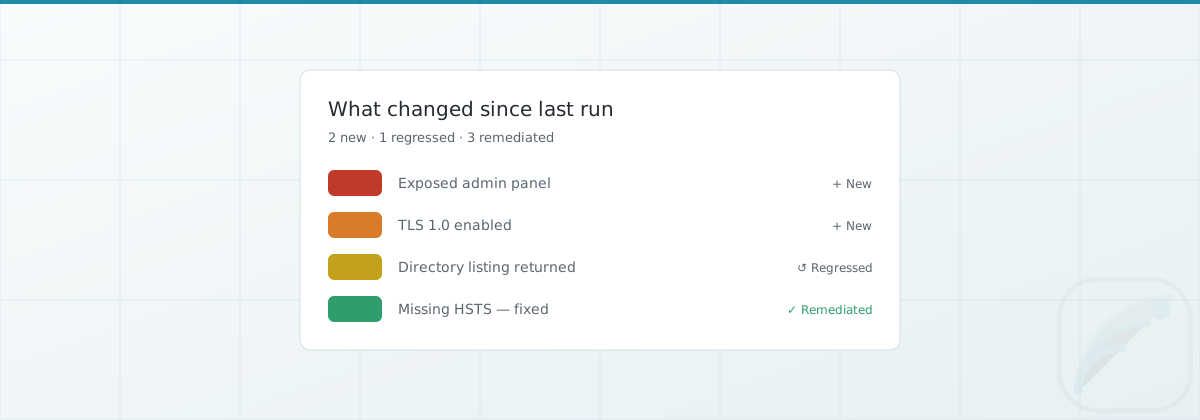
"What changed since last run" — the security report your execs will actually read
Turn on continuous scanning and you trade one problem for another. The annual pentest gave you a report nobody read until something broke. Continuous scanning gives you a firehose — and a 240-row findings export that nobody reads until something breaks. Congratulations, you’ve automated the ignoring.
The fix isn’t more scanning. It’s changing what you put in front of people. Because the valuable thing about running every day isn’t today’s full list — it’s the difference between today and last time.
The delta is the product
A good weekly report doesn’t open with “here are your 240 findings.” It opens with:
2 new (1 critical) · 1 regressed · 3 remediated · 1 new asset discovered
That’s a report a security lead reads in thirty seconds and a report you can hand to an executive without a translation layer. Every ProbeIQ scan produces exactly this: a diff against the previous completed run, bucketed into what’s new, what regressed, what got remediated, and which assets appeared that nobody told you about. The full inventory is still there for the person who needs to go deep — but the diff is what drives the weekly rhythm.
Triage once, not every run
A diff is only readable if it has memory. Run a raw scanner twice and the finding you marked “accepted risk” last week shows up as “new” again this week — so you re-triage the same noise forever, and real changes drown in it.
ProbeIQ gives findings persistent identity. A stable fingerprint collapses the same issue across engines into one finding, tied to the asset it lives on. When you triage it — confirmed, false positive, accepted risk — that decision sticks across scans. And a finding you marked remediated that comes back isn’t quietly re-listed; it’s flagged regressed, because a fix that didn’t hold is exactly the thing you want screaming at you.
That’s the difference between a cron job and attack-surface management: the cron job tells you what’s true today; ASM tells you what changed, and remembers what you already decided.
Four reports for four readers
Different people need different altitudes, so ProbeIQ produces:
- Executive summary — one page, plain language: your posture, and whether the trend is improving, holding, or regressing.
- Technical report — every confirmed finding, with CVSS and remediation guidance, for the people doing the fixing.
- Diff report — the “what changed since last run” view above; the thing people actually open each week.
- Asset inventory — hosts, services, technologies, certificates and their expiry dates, so nothing on your perimeter is a surprise.
Delivered where you already work
A report nobody sees is as useless as no report. ProbeIQ delivers in-app, by email digest, and to Slack or a generic webhook — plus downloadable JSON, CSV, and printable HTML when you need to attach something. You set the policy per scope: always, on change, or only above a severity threshold. No alert fatigue, no silence when it matters.
The weekly diff is the habit that makes continuous monitoring pay off. If your team is drowning in scanner output — or hearing nothing at all — see what a readable change report looks like.
Want this running against your own perimeter?Request early access →